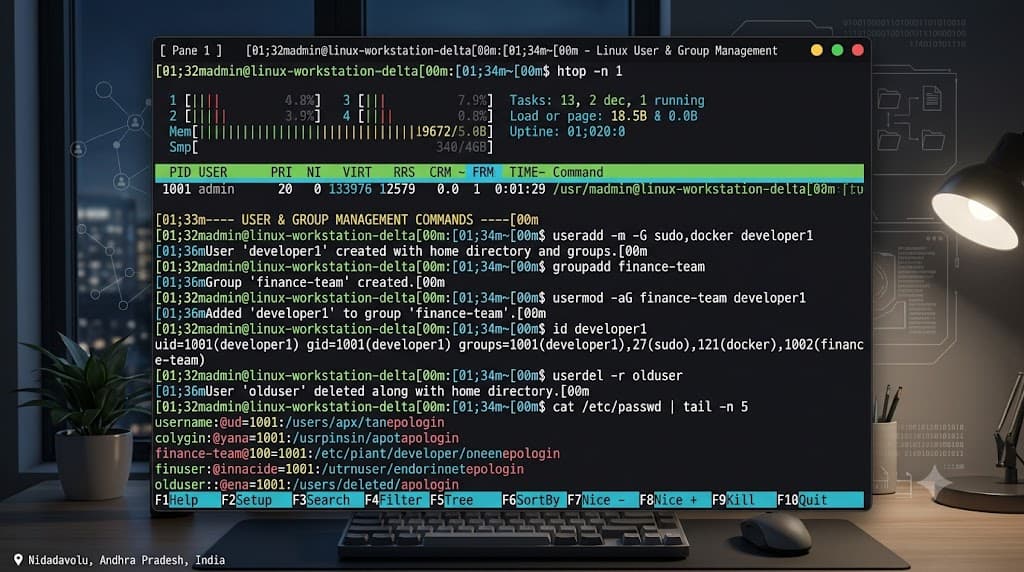
Quick Answer
Managing user accounts and access permissions is a fundamental responsibility for anyone administering a Linux environment, whether you are managing a bare-metal server, setting up a local development machine, or building secure container images. In multi-user systems, segregating users into specific groups allows administrators to enforce the principle of least privilege, ensuring that users and services only have access to the resources they genuinely require to perform their tasks. Whether you need to grant a developer access to the docker daemon, give a service account read permissions on a log directory, or manage SSH access via restricted groups, knowing how to properly modify group memberships is an essential skill.
Quick Answer
To quickly add an existing user to a secondary group in Linux, use the usermod command with the append flag. Open your terminal with administrative privileges and execute the following command:
sudo usermod -aG groupname username
If you need to add the currently logged-in user to a group without specifying their username explicitly, you can combine usermod with the whoami command:
sudo usermod -aG groupname $(whoami)
Alternatively, you can use the gpasswd utility to achieve the same result:
sudo gpasswd -a username groupname
After running either command, the user will typically need to log out and log back in, or restart their active session, for the updated group memberships to be fully recognized by all running processes and shell environments.
Understanding add user to group linux
To master user administration, you must first understand how Linux structures users, groups, and filesystem permissions. In GNU/Linux, every process is associated with a real user ID (UID) and a real group ID (GID), as well as effective IDs that determine immediate access rights to files, directories, and system calls. Groups in Linux are primarily used to organize multiple user accounts so they can share file permissions collectively without requiring individual permissions to be set for every single account.
Every user account has a primary group, which is typically assigned automatically when the user is created (often sharing the same name as the username in standard desktop distributions). In addition to this primary group, a user can belong to zero or more secondary groups, also referred to as supplementary groups. When a user creates a new file or directory, the primary group is usually stamped as the group owner of that file, whereas supplementary groups provide broader access rights to shared directories, development tools, and system daemons.
For developers and DevOps engineers, understanding this distinction is crucial when troubleshooting permission denied errors in shared environments, continuous integration servers, or containerized runners. If a build script cannot write to a shared cache directory or access a specific device file, checking group memberships is almost always the first diagnostic step. The operation to add user to group linux effectively extends a user's authorization profile, permitting them to participate in shared workflows governed by group-level file permissions.
How It Works
Behind the user-friendly command-line utilities, Linux manages user accounts and group memberships through a set of core configuration files residing in the /etc directory. Understanding these underlying files helps demystify what happens when you modify system permissions.
The most important files governing user and group databases are:
- /etc/passwd: Contains user account information, including usernames, encrypted passwords (historically, though now replaced by /etc/shadow), UIDs, primary GIDs, home directories, and default login shells.
- /etc/group: Defines the groups present on the system, listing the group name, encrypted password placeholder, GID, and a comma-separated list of members belonging to that group as secondary members.
- /etc/gshadow: Manages secure group data, including group passwords and administrators, ensuring that group modifications remain protected.
When you execute a command to modify group memberships, the operating system kernel updates these flat files or calls appropriate system libraries via Pluggable Authentication Modules (PAM). It is important to note that while /etc/group lists secondary members, a user's primary group is defined exclusively in /etc/passwd and does not appear in the member list of /etc/group. This architectural nuance trips up many administrators who check /etc/group and wonder why a user is missing from their primary group's listing.
Practical Commands and Examples
When working in a real-world Linux environment, you will rely primarily on two robust utilities to manage group memberships: usermod and gpasswd. Each tool provides specific flags and behaviors suited for different administrative scenarios.
Using the usermod Command
The usermod utility is the standard tool for modifying a user account's login properties. To add a user to a supplementary group without removing them from their existing groups, you must use the combination of the -a (append) and -G (groups) flags.
sudo usermod -aG developers alice
Let us break down this command:
- sudo: Executes the command with elevated root privileges, which are required to modify system-level user databases.
- usermod: The core user modification utility.
- -aG: The append (-a) flag combined with the secondary groups (-G) flag. Without the -a flag, usermod would remove the user from all other secondary groups not explicitly listed in the command, which can easily break user access.
- developers: The target group name you are adding the user to.
- alice: The target username.
You can also add a user to multiple groups simultaneously by providing a comma-separated list without spaces:
sudo usermod -aG developers,docker,wheel alice
Using the gpasswd Command
The gpasswd command is traditionally used for administering group files directly. It offers a straightforward syntax for adding and removing individual users from specific groups.
sudo gpasswd -a alice developers
In this example:
- -a: Adds the specified user (alice) to the specified group (developers).
Conversely, if you ever need to remove a user from a group using gpasswd, you can substitute the -a flag with the -d flag:
sudo gpasswd -d alice developers
Verification Commands
Never assume a command succeeded without verifying the state of the system. You can verify that a user has been successfully added to a group using several built-in commands.
The most direct way to check group memberships for a specific user is the groups command:
groups alice
Expected output:
alice : alice developers docker
Alternatively, you can query the id command, which displays the user ID, primary group ID, and all secondary group IDs:
id alice
Expected output:
uid=1001(alice) gid=1001(alice) groups=1001(alice),1005(developers),999(docker)
If you prefer inspecting the underlying configuration files directly, you can grep for the group name in /etc/group:
getent group developers
Expected output:
developers:x:1005:alice,bob
Common Mistakes
Even experienced developers and system administrators occasionally run into frustrating pitfalls when modifying Linux user permissions. Recognizing these common mistakes will save you hours of debugging.
Omitting the Append Flag (-a) with usermod
This is by far the most dangerous and frequent mistake made with usermod. If you run usermod -G developers alice without the -a (append) flag, Linux interprets your command as a replacement instruction. The operating system will remove alice from every single secondary group she previously belonged to, retaining only the 'developers' group. In a production environment, this can accidentally strip a deployment user of sudo privileges, Docker access, or deployment key permissions.
Assuming Group Changes Apply Instantly to Active Sessions
When you successfully modify a user's group memberships, the changes update the system databases immediately. However, Linux processes and shell sessions cache group memberships upon login. If a user is currently logged in via SSH or running an active terminal session, their current shell process will not reflect the new group memberships until they open a new session, log out and log back in, or spawn a new shell using the newgrp command.
Forgetting Administrative Privileges
Modifying system user databases in /etc requires root privileges. Running usermod or gpasswd without prefixing the command with sudo will result in permission denied errors or silent failures depending on the execution context.
Incorrect Group or Username Syntax
Typing a username or group name incorrectly will result in an error such as user 'alice' does not exist or group 'developers' does not exist. Always ensure the user and group exist before attempting modification, or create them using useradd and groupadd respectively.
Troubleshooting
When permissions fail despite executing the correct commands, a systematic troubleshooting approach is required. Consider a scenario where a developer has been added to the docker group to run containers without sudo, but running docker ps still returns a permission denied error.
Step 1: Verify System Database State
First, verify that the user is actually listed in the group database by running:
id
If the output does not display the target group in the groups list, the command was either not executed correctly or the system database has not updated.
Step 2: Check Active Session Group Cache
If the id command shows the group, but your current terminal session still rejects your commands, your active shell process has stale group credentials. You can refresh your current shell session's group list without logging out by invoking the newgrp command or switching user context:
newgrp docker
The newgrp command logs the current user into a new shell with the specified group as the active primary group, forcing the kernel to re-read the group memberships.
Step 3: Inspect Socket and File Permissions
Sometimes the issue is not the user's group membership, but the permissions on the target resource itself. For instance, Docker daemon sockets typically reside at /var/run/docker.sock. Inspect the file permissions using ls:
ls -l /var/run/docker.sock
Expected output showing correct group ownership:
srw-rw---- 1 root docker 0 Oct 10 12:34 /var/run/docker.sock
If the socket file is not owned by the expected group, modifying user group memberships will not resolve the access error until the service configuration or daemon permissions are corrected.
Best Practices
Maintaining a secure and auditable Linux environment requires adhering to established security principles and integrating user management practices cleanly into your broader development and DevOps workflows.
Adhere to the Principle of Least Privilege
Never add users to powerful system groups like root, wheel, or docker unless absolutely necessary. Granting unnecessary group memberships expands the attack surface of your application servers and development environments. For example, giving a standard developer unrestricted access to the docker group effectively grants them root-level access to the host system, as Docker containers can easily mount host filesystems.
Automate User Provisioning in Infrastructure as Code
In modern cloud environments, manual user management via terminal commands does not scale. When provisioning virtual machines, cloud instances, or CI/CD runner nodes, automate user and group creation using Configuration Management tools such as Ansible, Terraform, or cloud-init startup scripts. This ensures consistent security baselines across staging, testing, and production environments.
Managing Groups in Containerized and CI/CD Workflows
In containerized environments like Docker and Kubernetes, user management operates slightly differently. Containers often run as a specific non-root user defined in the Dockerfile using the USER instruction. If your CI/CD pipeline needs to build images or interact with shared volumes, ensure that the build user inside the container matches the UID and GID of the host runner user, or manage volume permissions explicitly using init containers or build arguments. Similarly, GitHub Actions self-hosted runners should be configured to run under dedicated service accounts with precisely scoped group memberships rather than running as the default root user.
📌 Recommended Next Guides & References
  <li>
    <a href="/article/docker-and-kubernetes-how-they-work-together-2" class="text-primary hover:underline font-semibold flex items-center gap-2">
      <span>→</span> <span>Docker and Kubernetes: How They Work Together</span>
    </a>
  </li>

  <li>
    <a href="/article/kubernetes-ingress-explained" class="text-primary hover:underline font-semibold flex items-center gap-2">
      <span>→</span> <span>Kubernetes Ingress Explained: Routing, Controllers, and TLS</span>
    </a>
  </li>

  <li>
    <a href="/article/kubernetes-ingress-controller-explained" class="text-primary hover:underline font-semibold flex items-center gap-2">
      <span>→</span> <span>Kubernetes Ingress Controller Explained: Architecture, Routing, and Implementation</span>
    </a>
  </li>


