Quick Answer
The terraform aws provider serves as the essential translation layer between your declarative Infrastructure as Code (IaC) configurations written in HashiCorp Configuration Language (HCL) and the actual AWS APIs. When you write resource definitions and execute commands via the Terraform CLI, the aws provider executes the underlying API requests to provision, modify, or destroy cloud resources such as Virtual Private Clouds, EC2 instances, S3 buckets, and IAM roles. Rather than interacting directly with the AWS Management Console or manually executing scripts, this provider maintains a local or remote state file that maps your configuration to real-world cloud entities, tracking dependencies and changes over time.
Quick Answer
The terraform aws provider is a specialized plugin for Terraform that enables engineers to manage and provision Amazon Web Services infrastructure declaratively. By defining desired states in HCL configuration files and executing CLI commands like plan and apply, the provider automatically calls AWS APIs to synchronize your actual cloud infrastructure with your code, handling dependency resolution and state tracking securely.
Understanding the Concept
Infrastructure as Code has fundamentally transformed how modern engineering teams build and manage cloud environments. Instead of relying on manual clickOps within the AWS console, teams define their entire cloud estate in code files that can be version-controlled, reviewed via pull requests, and tested prior to deployment. At the heart of this workflow is the concept of provider plugins. Terraform itself is a lightweight binary core; it does not inherently know how to talk to AWS, Google Cloud, Azure, GitHub, Docker, Kubernetes, or any other specific platform.
To bridge this gap, Terraform delegates platform-specific operations to external provider plugins. The aws provider is downloaded automatically during initialization and acts as the official driver for AWS. It understands the schemas, argument types, and API rate limits associated with hundreds of AWS services. Understanding how this architecture operates requires looking closely at how HCL defines resources and how provider versions are pinned to guarantee consistent, repeatable deployments across different environments and CI/CD pipelines.
Syntax and configuration
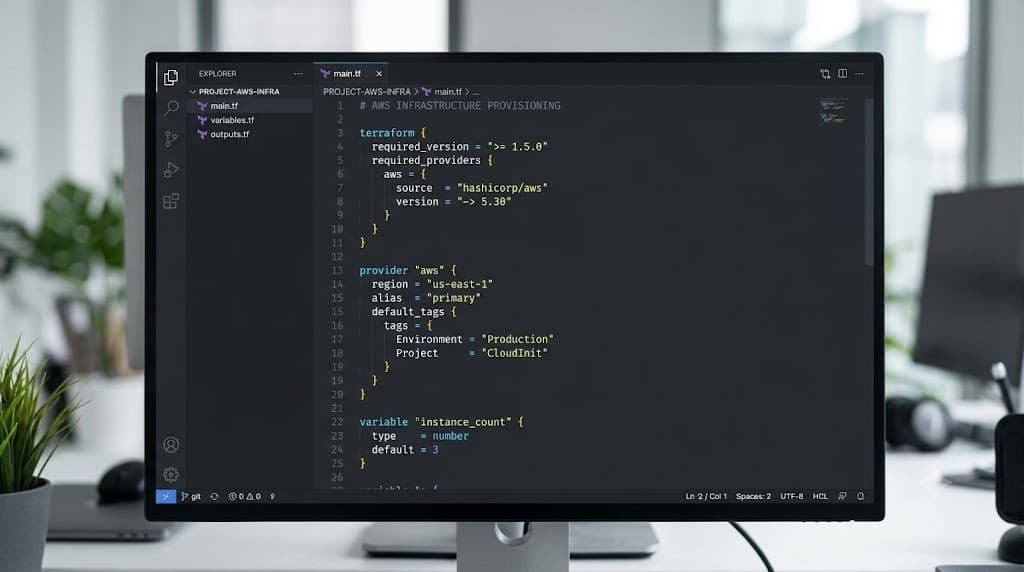
Configuring the aws provider requires declaring the provider block within your HCL files along with the necessary provider source registries and version constraints. Best practices dictate that you explicitly declare required providers in a required_providers block inside a terraform settings block. This prevents unexpected breaking changes when new provider versions are released.
terraform {
  required_version = ">= 1.5.0"
  required_providers {
    aws = {
      source  = "hashicorp/aws"
      version = "~> 5.0"
    }
  }
}

provider "aws" {
  region = "us-east-1"

  default_tags {
    tags = {
      Environment = "production"
      ManagedBy   = "Terraform"
    }
  }
}
In this configuration, the required_version attribute ensures that the executing Terraform CLI binary meets minimum version requirements. The aws provider block specifies the target AWS region (us-east-1) and applies default_tags across all resources managed by this provider instance. Critically, authentication credentials—such as AWS access keys and secret keys—are never hard-coded directly into the provider block. Instead, the provider automatically discovers credentials from standard environment variables like AWS_ACCESS_KEY_ID and AWS_SECRET_ACCESS_KEY, shared AWS credentials files, or attached IAM instance profiles and container roles, maintaining security best practices.
How It Works
The architectural mechanics of Terraform rely on a continuous loop of state evaluation, API translation, and resource reconciliation. When you define resources in HCL, Terraform compiles an internal graph of dependencies. For instance, if an EC2 instance depends on a specific subnet within a VPC, Terraform calculates that the VPC and subnet must be successfully created before the instance provisioning request can be sent to the AWS APIs.
As changes are applied, Terraform records the metadata and unique identifiers of created resources in a state file (commonly stored remotely in an S3 bucket with DynamoDB locking). During subsequent runs, Terraform refreshes this state by querying AWS to check if any external modifications occurred outside of Terraform. This state-driven model ensures that your declarative code remains the single source of truth for your cloud environment, preventing configuration drift and identifying discrepancies before they impact system stability.
CLI workflow
The foundational Terraform CLI workflow consists of a sequence of explicit commands designed to safely transition infrastructure from concept to reality. Understanding the distinction between these commands is vital for preventing accidental outages in production environments.
terraform init: Initializes the working directory, downloads required provider plugins like the aws provider, and configures backend state storage.terraform validate: Parses and checks configuration files for syntactic validity and internal consistency without contacting remote APIs.terraform plan: Generates and displays an execution plan, showing precisely which resources will be created, modified, or destroyed.terraform apply: Executes the actions proposed in the execution plan against the target AWS APIs after explicit user confirmation.terraform destroy: Removes all infrastructure managed by the current configuration state.
The most critical boundary in this workflow is between terraform plan and terraform apply. Running plan is a read-only operation that evaluates current state against desired HCL configuration and prints a clear diff. It introduces zero changes to AWS. Only when you execute apply does Terraform begin sending mutation requests to AWS.
Practical Terraform Example
To see the aws provider in action, consider a practical, real-world scenario: provisioning a secure Amazon S3 bucket along with a custom Virtual Private Cloud (VPC) network. Organizing your infrastructure code into logical modules or modular files helps maintain readability and scalability as your cloud architecture grows.
Example
Below is a complete, working HCL configuration example that provisions a private VPC and an encrypted S3 bucket. Follow these step-by-step instructions to set up your directory and execute the deployment.
First, create a file named main.tf and paste the following configuration:
terraform {
  required_version = ">= 1.5.0"
  required_providers {
    aws = {
      source  = "hashicorp/aws"
      version = "~> 5.0"
    }
  }
}

provider "aws" {
  region = "us-west-2"
}

resource "aws_vpc" "main" {
  cidr_block           = "10.0.0.0/16"
  enable_dns_hostnames = true
  enable_dns_support   = true

  tags = {
    Name = "production-vpc"
  }
}

resource "aws_s3_bucket" "app_logs" {
  bucket = "my-unique-application-logs-bucket-2026"

  tags = {
    Purpose = "Logging"
  }
}

resource "aws_s3_bucket_server_side_encryption_configuration" "logs_encryption" {
  bucket = aws_s3_bucket.app_logs.id

  rule {
    apply_server_side_encryption_by_default {
      sse_algorithm = "AES256"
    }
  }
}
To initialize your working directory and download the provider plugins, run the following initialization command in your terminal:
terraform init
Next, generate your execution plan to review the upcoming resource creation:
terraform plan -out=tfplan
Review the output to ensure Terraform intends to create exactly one VPC and one S3 bucket with server-side encryption enabled. Finally, apply the saved plan to execute the deployment:
<a href="/article/terraform-apply-create-and-update-infrastructure-2" class="text-primary font-semibold hover:underline">terraform apply</a> tfplan
Verification
Verifying that your infrastructure was provisioned correctly is a critical step in any deployment pipeline. You should never assume that an apply command succeeded without checking both the Terraform state and the actual AWS environment.
Verification
To confirm that your resources exist and are properly configured, you can utilize both Terraform CLI commands and the AWS CLI. First, inspect the local or remote state using Terraform show:
terraform show
This command outputs all attributes of the managed resources stored in your state file. To independently verify the deployment directly against AWS APIs, use the AWS CLI to describe the created VPC and list the S3 bucket:
aws ec2 describe-vpcs --filters "Name=tag:Name,Values=production-vpc"
aws s3api head-bucket --bucket my-unique-application-logs-bucket-2026
If the VPC description returns valid JSON containing your CIDR block and the S3 head-bucket command returns a successful exit status (0), your infrastructure has been successfully verified.
Common Mistakes
Working with Infrastructure as Code and cloud providers introduces specific operational hazards. Recognizing these frequent pitfalls helps prevent security incidents and deployment failures.
- Hard-coding credentials: Embedding AWS access keys or secret tokens directly inside
.tffiles exposes sensitive secrets in version control systems like GitHub. - Skipping terraform plan: Executing
terraform apply -auto-approvewithout reviewing the execution plan frequently leads to accidental deletions or unintended resource modifications. - Mismanaging state files: Storing state locally on a developer laptop in shared team environments causes state locking conflicts, race conditions, and catastrophic data loss if the machine fails.
- Using outdated provider versions: Failing to pin provider versions or lagging far behind current releases can expose you to unpatched bugs and breaking schema changes.
Failure modes
When utilizing the aws provider, engineers frequently encounter specific error messages and failure states. One common issue is an authentication failure, signaled by errors such as NoCredentialProviders: no valid providers in use. This occurs when the AWS CLI credentials file is missing, environment variables are unset, or an expired IAM session token is active. Another frequent failure mode is resource naming collision, such as BucketAlreadyExists, which happens when an S3 bucket name is globally claimed by another AWS account. Resolving these requires updating your HCL configuration to use a globally unique naming convention or incorporating random suffix generators.
Best Practices
Deploying infrastructure to production requires robust operational guardrails. Always store your state remotely in an encrypted Amazon S3 bucket with state locking enabled via Amazon DynamoDB to prevent concurrent modifications by multiple engineers or CI/CD systems. Utilize IAM roles with least-privilege permissions for your deployment pipelines rather than long-lived administrator access keys.
Furthermore, structure your code into reusable modules, enforce automated formatting via terraform fmt, and run static analysis tools like tflint or security scanners like tfsec within your continuous integration pipelines before any pull request is merged.
Troubleshooting
When deployments fail or unexpected drift occurs, structured troubleshooting is essential to identify root causes quickly. Begin by increasing logging verbosity to inspect the exact API requests and responses passing between Terraform and AWS.
Troubleshooting
To debug complex issues with the aws provider, enable verbose logging by setting the environment variable before running your command:
export TF_LOG=DEBUG
export TF_LOG_PATH=terraform_debug.log
terraform apply
Examine the generated terraform_debug.log file to inspect HTTP status codes returned by AWS APIs. If you encounter 429 Too Many Requests errors, you are hitting AWS rate limits and should introduce retry logic or stagger resource creation. If resources appear out of sync, run terraform refresh or use <a href="/article/terraform-import-bring-existing-infrastructure-under-management" class="text-primary font-semibold hover:underline">terraform import</a> to reconcile existing cloud objects with your HCL state file.
📌 Recommended Next Guides & References
  <li>
    <a href="/article/docker-and-kubernetes-how-they-work-together-2" class="text-primary hover:underline font-semibold flex items-center gap-2">
      <span>→</span> <span>Docker and Kubernetes: How They Work Together</span>
    </a>
  </li>

  <li>
    <a href="/article/kubernetes-ingress-explained" class="text-primary hover:underline font-semibold flex items-center gap-2">
      <span>→</span> <span>Kubernetes Ingress Explained: Routing, Controllers, and TLS</span>
    </a>
  </li>

  <li>
    <a href="/article/kubernetes-ingress-controller-explained" class="text-primary hover:underline font-semibold flex items-center gap-2">
      <span>→</span> <span>Kubernetes Ingress Controller Explained: Architecture, Routing, and Implementation</span>
    </a>
  </li>


