Quick Answer
Managing system access and authorization correctly is a fundamental requirement for anyone building, deploying, or maintaining production environments. Understanding how the operating system handles identity is essential for maintaining a secure and stable infrastructure, whether you are provisioning a bare-metal server, hardening a cloud virtual machine, or containerizing applications. This guide provides an in-depth, practical look at how Linux identities work, how to execute administrative tasks safely, and how these underlying primitives intersect with modern developer workflows.
Quick Answer
Linux users are distinct system accounts defined by a unique numeric identifier called a User ID (UID). Each account holds specific permissions determining what files it can read, write, or execute, and what processes it can run. Linux groups are collections of user accounts sharing common access privileges, allowing administrators to manage permissions for multiple accounts simultaneously rather than modifying individual files for every single person. The Linux kernel evaluates these identities at runtime against file ownership metadata to enforce strict access control, ensuring that unprivileged accounts cannot alter critical system binaries or access confidential configuration data.
Understanding linux users
Every single process and file on a Linux operating system is owned by a specific account and associated with a primary group. When you log into a terminal shell via SSH or open a local console, the operating system assigns your session an active User ID (UID) and a primary Group ID (GID). These numeric values dictate every permission check performed by the Linux kernel when you attempt to interact with the filesystem, send signals to running processes, or bind to network ports.
The Superuser Account and Root Privileges
At the pinnacle of the system identity hierarchy sits the root account, bearing a UID of 0. The root user bypasses standard discretionary access control checks, holding absolute administrative authority over the entire operating system. While essential for system installation, package management, and low-level kernel configuration, running daily development or deployment tasks as root introduces massive security risks. A single accidental command or a compromised application running with UID 0 can wipe critical system directories or compromise the entire host. Modern administrative patterns rely instead on standard unprivileged accounts paired with privilege escalation tools like sudo to execute specific commands with elevated privileges only when strictly necessary.
System Users vs. Regular Users
Standard distributions divide accounts into two major categories: regular human users and system accounts. Regular users typically have UIDs starting at 1000 and are assigned interactive login shells such as /bin/bash or /bin/zsh. System accounts, conversely, often feature lower UIDs (such as 1 to 999) and are assigned non-interactive shells like /sbin/nologin or /bin/false. These accounts exist to run background daemons and network services—such as web servers, database engines, or monitoring agents—ensuring that if a specific daemon is compromised, the attacker gains access only to that service's limited filesystem footprint rather than the entire system.
How It Works
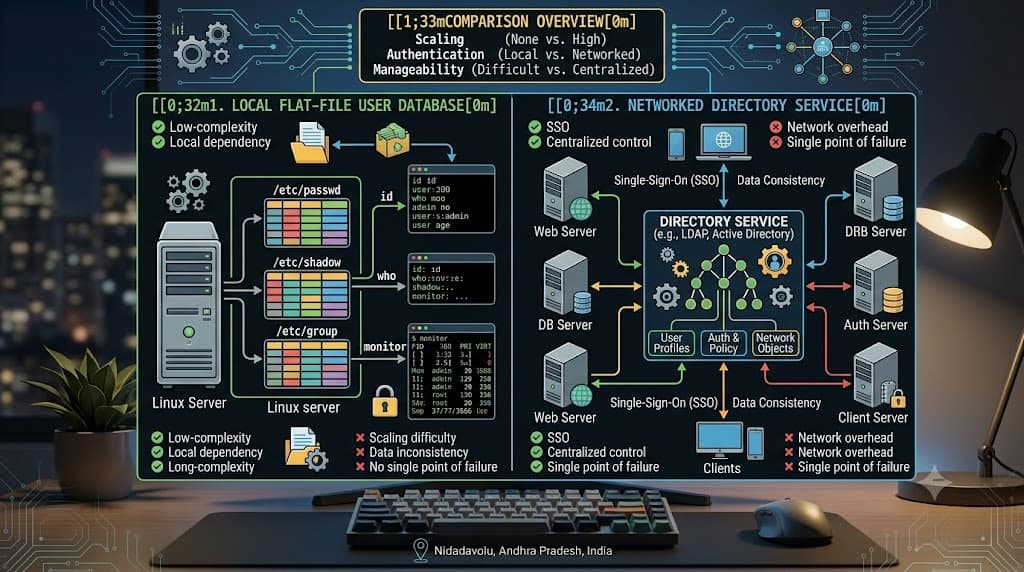
To understand how the operating system resolves these identities under the hood, we must examine the core configuration files located in the /etc directory. These text-based configuration files form the backbone of local identity management on standard Linux distributions.
The /etc/passwd File Explained
Every local account is represented by a single line in the /etc/passwd file. Despite its historical name, this file no longer stores actual passwords. Instead, it acts as a public database mapping account names to their numeric identifiers, home directories, and default shells. Each line consists of seven colon-delimited fields:
- Username: The login name used by the account.
- Password placeholder: Historically stored the encrypted password hash, but now universally represented by an 'x', indicating that the actual hash is securely stored elsewhere.
- UID: The unique numeric identifier assigned to the account.
- GID: The numeric identifier of the account's primary group.
- GECOS field: Descriptive user information, such as full name or contact details.
- Home directory: The absolute path to the account's default working directory.
- Shell: The path to the executable program launched upon interactive login.
The /etc/shadow File and Security
Because the /etc/passwd file must be readable by standard utilities so that applications can resolve usernames, storing password hashes inside it would pose a significant security risk to brute-force attacks. Consequently, modern Linux distributions store encrypted password hashes and aging parameters in /etc/shadow. This file is restricted and can only be read by processes running with root privileges, protecting credential hashes from unprivileged inspection.
The /etc/group File and Group Memberships
Groups are managed through the /etc/group file, which maps group names to their numeric Group IDs (GIDs) and lists the secondary members belonging to each group. Each line in this file contains four colon-delimited fields: the group name, the group password placeholder (typically 'x'), the numeric GID, and a comma-separated list of usernames belonging to that group as secondary members. When an account is created, it is typically assigned a primary group matching its username, and can be added to any number of secondary groups to inherit shared file access permissions.
Practical Commands and Examples
Administrators and engineers interact with system identities through standard command-line utilities. Knowing the correct syntax and flags prevents misconfigurations and ensures smooth environment provisioning.
Creating and Managing Accounts
The useradd command is the low-level utility used to create new system accounts, while userdel handles their removal. When provisioning an interactive developer account, administrators typically combine several flags to set up the home directory and default shell correctly.
sudo useradd -m -s /bin/bash -c "Developer Account" devuser
In this example, the -m flag instructs the utility to create the user's home directory under /home/devuser, the -s flag assigns the Bash shell, and the -c flag adds a descriptive comment. To verify that the account was created successfully, inspect the tail of the password database:
getent passwd devuser
Managing Group Memberships
To grant an account access to shared resources without modifying primary ownership, you must add user to group linux administrators manage. The standard and safest way to modify supplementary group memberships without overwriting existing assignments is using theusermod utility with the append flag.
sudo usermod -aG developers devuser
The -a flag stands for append, and the -G flag specifies the supplementary group list. Omitting the -a flag would accidentally remove the user from all other secondary groups they previously belonged to, making this flag combination critical for safe administrative work.
Verifying Group Memberships
After modifying group assignments, the changes do not automatically propagate to currently active login sessions because group memberships are loaded into kernel memory upon session initialization. To verify that the membership was correctly written to the system databases, use the groups command or query the group database directly:
groups devuser
getent group developers
If an active user session needs to pick up new group memberships immediately without logging out and back in, the user can spawn a new shell session using their updated group context:
newgrp developers
Common Mistakes
Even experienced engineers occasionally make errors when managing system access and permissions. Recognizing these common pitfalls helps prevent security gaps and broken deployments.
Overwriting Secondary Groups with usermod
A frequent mistake when attempting to add user to group linux configurations is running usermod -G groupname username without the -a (append) flag. Because the -G flag replaces the entire list of supplementary groups rather than adding to it, executing this command incorrectly strips the account of all its previous group memberships, breaking access to shared source repositories, database utilities, and deployment tools.
Running Application Workloads as Root
Another critical mistake is configuring custom application services, background daemons, or CI/CD build agents to run directly as the root user. While this eliminates immediate permission denial errors during file writes, it violates the principle of least privilege. If an application vulnerability or dependency exploit allows remote code execution, the attacker immediately gains full administrative control of the underlying host machine.
Neglecting UID and GID Consistency Across Shared Storage
When managing clusters or network filesystems shared across multiple virtual machines, administrators sometimes create local accounts manually without specifying explicit UIDs or GIDs. If user 'alice' has UID 1001 on server A but UID 1002 on server B, file permissions stored on Network File System (NFS) mounts or shared volumes will misalign completely, leading to mysterious permission denial errors.
Troubleshooting
When permission errors or authentication failures occur in production or staging environments, a systematic troubleshooting approach helps isolate and resolve the root cause quickly.
Diagnosing Permission Denied Errors
When a process or user encounters a permission denied error, the first step is inspecting the exact ownership and permission bits of the target file or directory using the long listing format.
ls -la /var/www/html
Examine the output to verify whether the file is owned by the expected user or group, and whether the permission triad (read, write, execute) grants access to the relevant category (owner, group, or others). If necessary, adjust ownership safely using the chown utility rather than granting overly permissive world-write permissions:
sudo chown -R www-data:www-data /var/www/html
Investigating PAM and Authentication Logs
If an account cannot log in via SSH or sudo, authentication failures are logged by Pluggable Authentication Modules (PAM) and systemd-logind. You can inspect recent authentication events in real-time using the system logging utility:
sudo journalctl -u ssh -n 50 --no-pager
This output reveals whether the failure stems from missing public keys, expired credentials, locked accounts, or shell misconfigurations.
Best Practices
Integrating robust identity management into your wider software development lifecycle ensures that security is maintained from local development through containerized deployments and CI/CD pipelines.
Enforcing the Principle of Least Privilege
Every process, container, and developer account should operate with the absolute minimum set of privileges required to complete its task. In containerized environments such as Docker, explicitly define non-root execution contexts within your Dockerfile:
FROM ubuntu:24.04
RUN useradd -u 10001 -m appuser
USER appuser
CMD ["./app"]
By creating a dedicated non-root user and switching to it via the USER directive, you prevent container breakout vulnerabilities from compromising the host kernel.
Managing Identities in Kubernetes and CI/CD
In Kubernetes deployments, security contexts play a role analogous to traditional system identities. Always configure securityContext in your Pod and container specifications to enforce non-root execution and drop unnecessary Linux capabilities:
securityContext:
  runAsNonRoot: true
  runAsUser: 10001
  allowPrivilegeEscalation: false
Similarly, in GitHub Actions and other CI/CD pipelines, ensure that custom build steps or self-hosted runner agents do not execute untrusted build scripts with root privileges. Running build jobs under restricted service accounts prevents malicious pull requests from altering runner configurations or leaking environment secrets.
📌 Recommended Next Guides & References
  <li>
    <a href="/article/docker-and-kubernetes-how-they-work-together-2" class="text-primary hover:underline font-semibold flex items-center gap-2">
      <span>→</span> <span>Docker and Kubernetes: How They Work Together</span>
    </a>
  </li>

  <li>
    <a href="/article/kubernetes-ingress-explained" class="text-primary hover:underline font-semibold flex items-center gap-2">
      <span>→</span> <span>Kubernetes Ingress Explained: Routing, Controllers, and TLS</span>
    </a>
  </li>

  <li>
    <a href="/article/kubernetes-ingress-controller-explained" class="text-primary hover:underline font-semibold flex items-center gap-2">
      <span>→</span> <span>Kubernetes Ingress Controller Explained: Architecture, Routing, and Implementation</span>
    </a>
  </li>